In progress · Private
WordPress Website Security Auditor
A private internal tool that audits WordPress Core and active plugins against live version and CVE information.
Problem
WordPress sites often accumulate plugins over time, making it tedious to confirm that WordPress Core and every active plugin are current and free of known security issues.
What I built
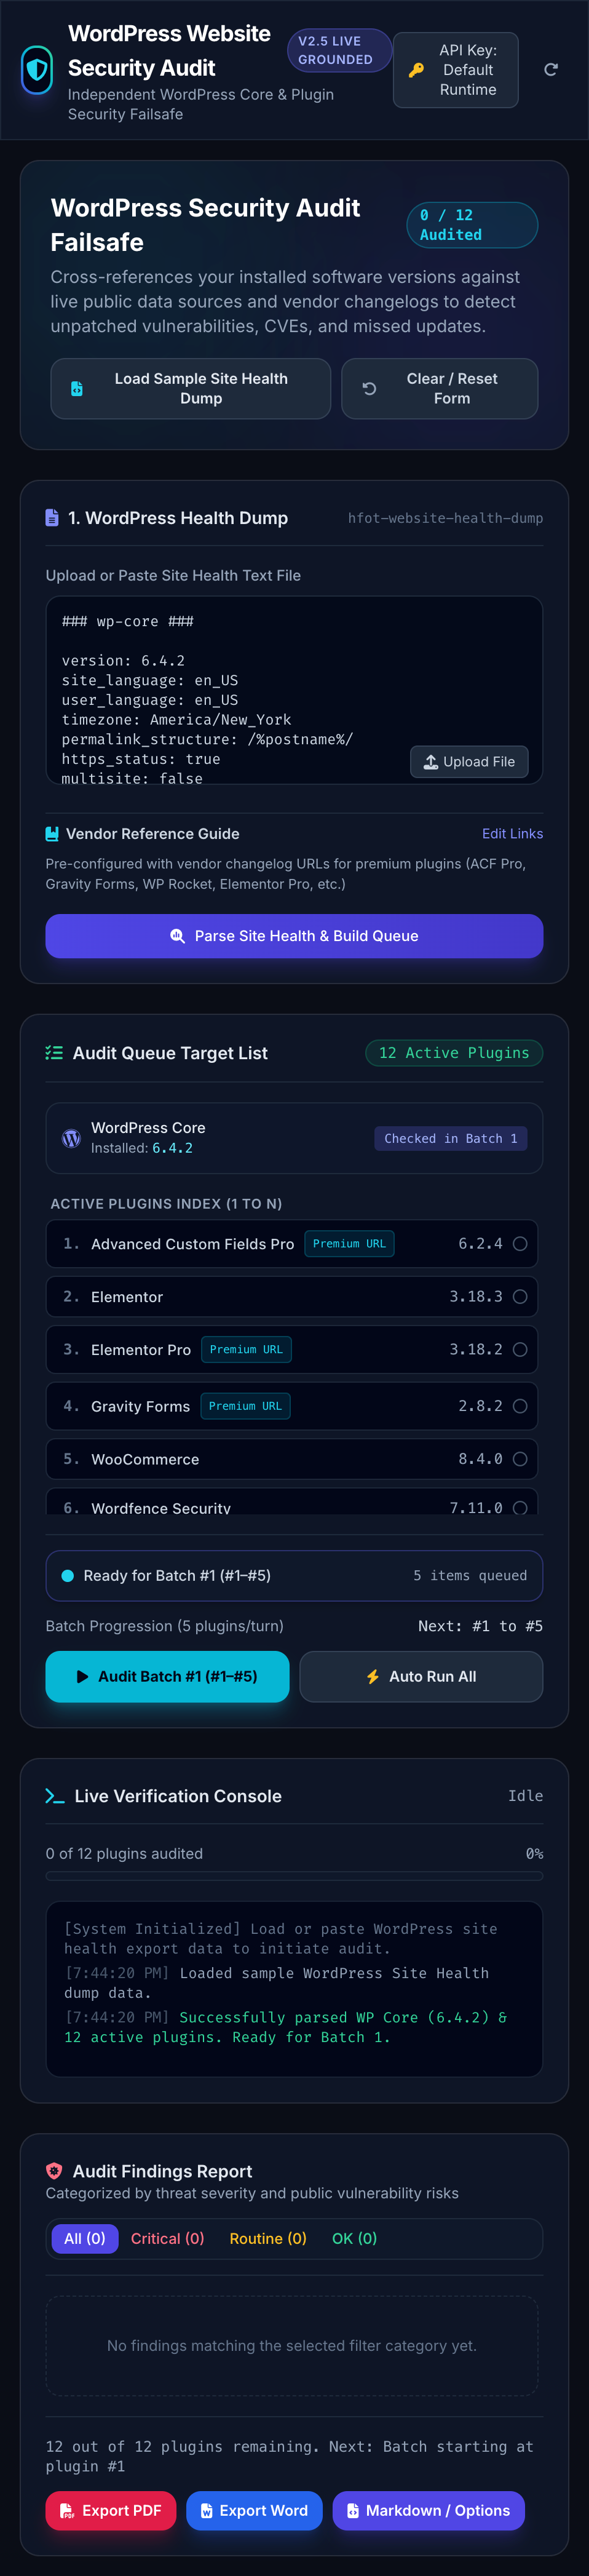
An internal WordPress Website Security Auditor that turns a WordPress Site Health export into a structured security report. It focuses on outdated software and known CVE vulnerabilities in WordPress Core and active plugins.
How it works
The tool ingests the Site Health text export, which lists installed software and versions. It sends that information to Google Gemini with live Google Search Grounding enabled. Gemini then cross-references each item with current public sources such as official plugin repositories, CVE databases, and changelogs.
The resulting report is structured and color-coded, with export options for sharing or follow-up work.
Technologies
WordPress Site Health exports, Google Gemini, Google Search Grounding, official plugin repositories, CVE databases, and changelogs.
Screenshots and visuals
What I learned
Live source checking can make an audit more useful than relying only on a static vulnerability database, especially when version and changelog information changes frequently.
Results and status
In progress as a private internal tool. It is designed to support a faster, more current WordPress security review workflow.